AI can strengthen protection by finding patterns across security data, prioritizing suspicious activity, and helping teams respond faster. For organizations facing growing threats, that speed can help security teams spot risk across large amounts of data. Yet a model can miss context or flag normal work as dangerous. Alert triage is the process of sorting security alerts by risk and deciding which ones need investigation first.
When you consider how to use AI in cybersecurity, think of it as support for your security team, not a replacement for its judgment. AI can help staff review more signals and focus on the events that may matter most. People still need to check important findings and decide how to act. AI recommendations need human verification before they drive consequential decisions.
Key Takeaways
- Use AI to sort signals and surface patterns across security data.
- Connect AI recommendations to approved policies and clear ownership.
- Check unusual behavior against related signals before confirming a threat.
- Measure false positives and analyst workload, not speed alone.
- Test models on the task and data your organization actually needs.
- Start with one workflow and expand only after reviewing its results.
Treat every AI recommendation as a lead to verify, not proof that an incident is real.
How to Use AI in Cybersecurity Across a Defense Cycle
A useful AI defense cycle starts by detecting an unusual signal, then adds context before recommending an action. The cycle connects artificial intelligence to the systems your team already uses, rather than treating AI as a separate security program. Context matters because one event can look risky alone and routine beside related activity.
AI identifies patterns or recommends a decision; automation carries out an approved action. Machine learning finds patterns in prior data, while deep learning handles more complex patterns. Natural language processing, or NLP, processes text such as emails, reports, and policy documents.
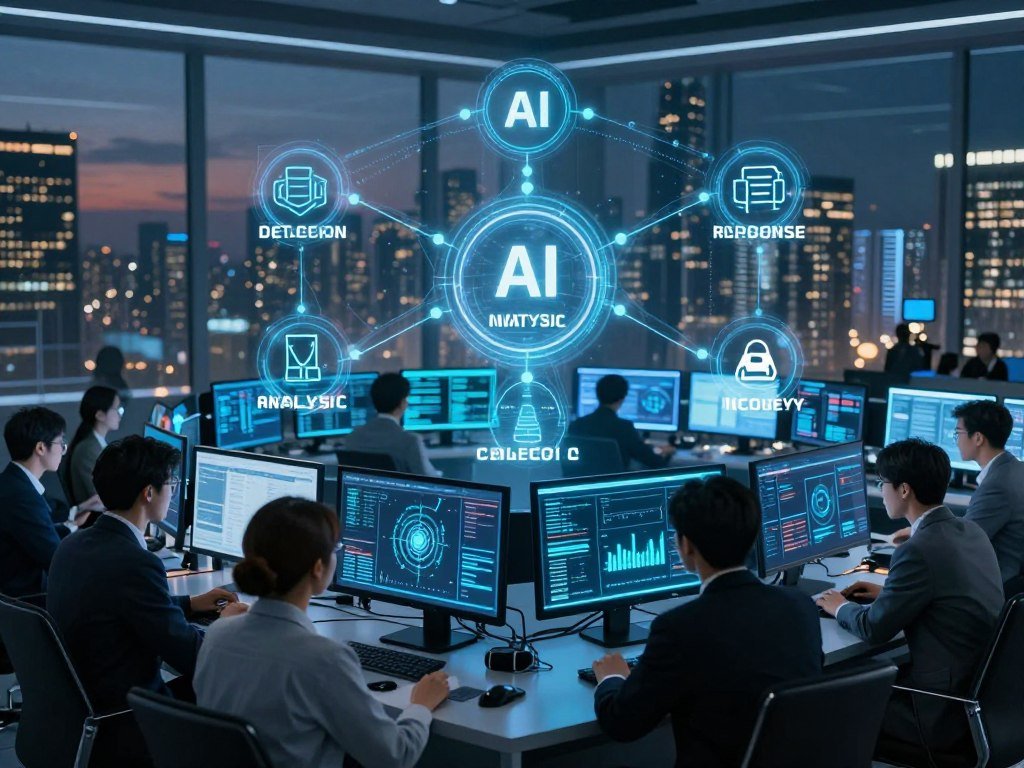
- Detection: Find a signal that differs from expected activity.
- Analysis: Add identity, asset, and threat intelligence context.
- Decision: Recommend a response that fits the risk and policy.
- Response: Carry out an approved action and track its result.
Use AI to detect and analyze security signals
AI can scan security data from multiple systems and rank events for review. It can also help compare evidence with known risks and draft a summary for an analyst. A person checks whether the evidence supports the recommendation before deciding what it means.
NIST’s August 19, 2026, draft quick-start guide describes ways GenAI can help analyze, plan, implement, and monitor progress toward Cybersecurity Framework 2.0 outcomes. Its prompts cover policy and governance review, mapping evidence to a draft current-state profile, and creating a draft target-state profile. The NIST draft quick-start guide presents these prompts and use cases as illustrative, not as prescriptive assessment or assurance methods.
Connect recommendations to response and recovery
A recommendation becomes useful when it leads to a response your team can track. Automation might open a case, block a connection, or isolate a device, depending on the approved workflow. Recovery restores operations, checks what failed, and feeds lessons back into security systems.
Keep each automated action tied to an existing security policy and a named human owner.
That owner should know which system will act and how the team will review the result. NIST’s voluntary AI Risk Management Framework addresses AI risks and trustworthiness across design, development, use, and evaluation.
Where Can AI Find Threats Before They Spread?
A familiar-looking login can become suspicious when its device, location, or access pattern suddenly changes. AI can compare security signals across messages, accounts, devices, and networks to help find threats earlier. A change in context can matter more than a single event.
An anomaly is a prompt for investigation, not proof of compromise. Machine learning can detect activity that lacks a known signature, which helps when threat intelligence has not yet identified a new attack. Security teams still need to check related evidence.
Spot suspicious messages and login attempts
Email analysis can assess a sender, domain, wording, and message context for signs of phishing. A message that copies a real business style may still use a strange domain or ask for an unusual action. AI can flag the mix of signals for review.
Authentication systems can also consider device details, location, and login history. A sudden change may prompt another check, such as a fresh sign-in challenge. The same travel pattern can be normal for one worker and unusual for another.
Find behavioral anomalies across users and devices
User and entity behavior analytics, or UEBA, compares current activity with profiles for users, devices, and servers. It may flag a service account that accesses new systems or a device that sends data at an unusual time. Such alerts help analysts spot behavior that a fixed rule might miss.
Fast detection matters because attackers can move quickly after gaining access. The fastest eCrime breakout time in 2025 was 27 seconds, and average breakout speed rose 65% year over year. Those figures make rapid review useful, but speed alone cannot confirm an incident.
Contain suspicious endpoint and network activity
Endpoint tools can flag unusual file behavior, while network detection and response, or NDR, can spot strange traffic or lateral movement. These tools can bring together signals that might look harmless in isolation. A configured response policy may isolate a device when evidence meets its threshold.
Edge devices deserve close attention because they connect internal systems to outside networks. In 2025, 40% of vulnerabilities exploited by China-nexus adversaries targeted edge devices. Check the event against related identity, endpoint, and network signals before escalating it as a confirmed threat.
The 2025 breakout and edge-device figures show why both speed and exposure deserve attention, without making every anomaly an incident.
Which AI Tools Fit Security Operations?
The right AI security tool is the one that improves a defined workflow using data the team can trust. Security operations teams can find AI across several tool types, each built to monitor different data. Start with the workflow, not a product label.
Measure alert quality and analyst workload alongside response speed. Faster triage can help analysts spend less time sorting routine events. Broader monitoring can reveal activity across more systems, while automation can cut repetitive manual steps.
Match security tools to the data they monitor
Use this table to match a tool category with its data and typical action. A tool that sees only one part of your environment may miss context held elsewhere.
| Tool category | Data monitored | Typical AI task | Example action |
|---|---|---|---|
| Endpoint protection | Device and file activity | Flag suspicious behavior | Alert or isolate under policy |
| Next-generation firewall | Network traffic and applications | Inspect and classify traffic | Block or inspect a connection |
| SIEM and SOAR | Alerts and logs across tools | Correlate, triage, and run workflows | Open a case or trigger an approved playbook |
| Cloud security | Cloud configurations and activity | Flag risky settings or data flows | Alert or recommend a fix |
| NDR | Network traffic | Find anomalies and lateral movement | Raise an investigation |
A security information and event management system, or SIEM, collects and reviews security logs. Security orchestration, automation, and response, or SOAR, links alerts to response workflows. Together, these systems can help teams connect events across tools.
Measure whether the workflow helps analysts
AI use in cybersecurity strategies rose from 50% in 2025 to 78% in 2026, while 27% described deployment as mature production. Adoption alone does not show whether a workflow works well. Track how often alerts prove useful and how much time analysts spend checking them.
False positives can consume the time a tool was meant to save. Compare the volume of useful cases with the extra review work, and check whether analysts can explain why a recommendation appeared. Compare alert quality and investigation time before expanding a tool to more systems.
What Does Generative AI Add, and How Do Attackers Misuse It?
GenAI can draft a useful incident summary, but the same ability to produce convincing content can make fraud harder to spot. Security teams can use generated text to support analysis, training, and response planning. Review remains essential because generated content can sound certain while getting details wrong.
Generated content needs review before it guides a security decision. Synthetic training examples can help staff practice, but they should not replace tests with real systems and validated data. A polished summary is still a draft.

Use GenAI for simulations, summaries, and analyst support
Teams can use GenAI to draft attack simulations, create synthetic data for training, and summarize incident timelines. It can also suggest mitigation steps for an analyst to assess. These uses can reduce the time spent preparing materials and reviewing long records.
Simulations should reflect the systems and risks your organization faces. Synthetic examples may help staff learn, yet they cannot prove that a real control will work under pressure. An analyst should check the facts and test suggested fixes before use.
Recognize AI-enabled fraud and influence attempts
Attackers can use AI to scale convincing phishing, scams, influence operations, and deepfakes. In a reported Arup fraud, generated video and voice impersonations appeared during a live call, and staff authorized a reported $25 million payment. A familiar face or voice is not independent verification.
Anthropic’s September 2026 report describes malicious activity involving Claude that the company identified and disrupted between December 2025 and August 2026. It covers seven harm areas, including cyber operations, influence operations, surveillance, scams and fraud, biological misuse, conventional weapons development, and distillation. Reported U.S. losses from cyber-enabled crime reached nearly $21 billion in 2025.
Reviewing generated video for errors is a useful habit beyond security, especially when a clip may shape a decision.
Set boundaries around generated output
Keep GenAI away from decisions that require evidence it cannot access or check. A summary can omit a key event, and a recommendation can rely on incorrect assumptions. Give analysts the original records alongside any generated explanation.
Verify payment and account-change requests through a separate trusted channel, even when a live video call appears genuine.
How Can AI Prioritize Vulnerabilities and Exposure?
A long vulnerability list becomes actionable when exploit evidence is combined with the value and exposure of each asset. AI can help rank risk by linking threat intelligence to asset records and network context. Asset context turns a raw score into a decision.
Use rankings to guide review, not to replace asset ownership and business judgment. A high-severity flaw on an isolated test system may pose less risk than a known exploited flaw on an internet-facing service. The right fix depends on access, business role, and attack paths.
Rank vulnerabilities by exploitability and asset importance
Use these steps to turn a vulnerability queue into assigned work:
- Confirm who owns the asset and how important it is to the business.
- Check whether it faces the internet or connects to critical systems.
- Compare severity with known exploitation and current threat intelligence.
- Assign a fix, mitigation, or accepted-risk decision to an owner.
The CISA Known Exploited Vulnerabilities catalog is one useful input, not a complete risk score. Teams should also consider whether a flaw affects a system attackers can reach and whether a safe workaround exists.
New vulnerabilities were exploited in an average of 4.76 days, 43% faster than in the preceding period. Cloud-conscious intrusions by state-nexus threat actors increased 266% in 2025. These trends make current exposure data important when setting repair order.
Map risks across cloud, network, and operational technology
Cloud services, network devices, and operational technology, or OT, often depend on links between assets. A cloud account may reach a data store, while an OT control system may connect to a fragile production line. AI rankings work better when those relationships appear in the inventory.
Active scans can disrupt some fragile OT systems, so passive monitoring may be safer. Teams can use network traffic and configuration records to map exposure without probing every device. In 2025, 40% of vulnerabilities exploited by China-nexus adversaries targeted edge devices.
Fix gaps in the asset inventory before trusting automated priority rankings.
How Do You Keep AI Decisions Safe and Accountable?
Safe automation starts by deciding which errors the organization can tolerate and which actions require a person’s approval. AI can make incident response faster, but poor data, privacy gaps, or a prompt injection can lead to harmful output. Set limits before rollout, while the system’s role remains small.
Require analyst approval for disruptive or high-impact response actions. Inaccurate or biased training data can skew results, and false positives can interrupt normal work. Over-reliance can also turn a wrong recommendation into a larger mistake.
Protect data and test for model failure
Limit sensitive data sent to models, especially personal details and private business records. A prompt injection can try to steer a model through hostile text inside an email, document, or web page. Test how the system handles both ordinary work and attack attempts.
- Limit sensitive data sent to models.
- Test with representative normal and attack activity.
- Log model inputs, outputs, and resulting actions.
- Require analyst approval for disruptive or high-impact response.
- Review errors and permissions on a set schedule.
Cybersecurity professionals who use AI report extra work to judge its advice: 65% spent more time deciding whether to trust or act on recommendations, and 63% spent more time reviewing outputs. That review is part of the workload, not a sign that the tool has failed.
Set human approval levels for response actions
Some actions can run under a clear policy, such as opening a case or collecting more logs. Blocking a user account or isolating a critical device can disrupt business, so those actions need an approval path. Make the allowed action and its owner clear to staff.
In a May 2026 survey, 62% worried about over-reliance on recommendations, and 61% worried about errors spreading across systems. Also, 89% said their organizations had experienced incorrect AI recommendations. Only 50% said human decision-makers were ultimately accountable for outcomes caused by AI-recommended actions.
Govern AI use with clear ownership
NIST released its AI Risk Management Framework 1.0 on January 26, 2023, and its Generative AI Profile, NIST-AI-600-1, on July 26, 2024. A 2026 concept note proposed a critical-infrastructure profile for trustworthy AI. The voluntary framework can help structure risk management and trustworthiness.
NIST’s AI prompts remain illustrative, not assurance methods. CISA’s roadmap covers responsible internal AI use, AI assurance, protection of critical infrastructure, collaboration, and workforce expertise. Practitioners named behavioral detection at 48%, user awareness training at 45%, human analyst review at 39%, and AI-specific security controls at 23% as effective defenses.
A workflow-based review of AI tools also stresses data terms, access controls, and human approval. C-suite confidence in AI outputs was 67%, compared with 21% among managers.
Keep a named human accountable for every automated action that could disrupt access or business operations.
How Should You Evaluate AI Cybersecurity Models?
A model can lead on one cybersecurity benchmark and still perform poorly on a different task. Compare models by the job you need them to do, such as patching code or resisting prompt injection. One score cannot cover every task.
Use benchmark results to screen models, then test them with your own data and approval controls. Results depend on the task, data, and scoring method. A strong result on one test does not prove accuracy across security work.
Compare models only on the task you need
The benchmarks below measure different abilities, so their scores are not direct competitors.
| Benchmark | Task measured | Result | What the result does and does not show |
|---|---|---|---|
| CWE-bench v1 | Defensive vulnerability patching | Google scored 68% across 120 held-out tasks and 73 weakness types | Patching performance on that task set |
| ExploitBench | Full-control V8 exploit synthesis | Claude Mythos 5 scored 78% across 16 capability flags | Exploit capability, not defensive patching |
| Gray Swan IPI | Indirect prompt-injection attack success | 15 attempts; lower scores mean greater resistance | Tested attack resistance, not overall model quality |
Advanced cyber completion rate measures whether a model completes approved advanced-cyber requests rather than refusing them. It does not measure cybersecurity skill. Google’s Argon for cyber defenders reached the Gemini app for Google AI Pro and Ultra on October 13, 2026.
Validate benchmark results in your own environment
A strong research paper on artificial intelligence in cyber security should state its task, dataset, baseline, error rates, and validation limits. University of Maryland researchers found that 25% of agent-generated patches were substantially similar to historical developer fixes. They also found that one proof-of-concept test inflated patching solve rates by an average of 1.83 times across 11 agents.
The PatchBench evaluation study describes tests across 213 tasks, 16 CWE types, and 32 real-world projects. It checks whether a patch removes a weakness while preserving expected behavior.
Research results can help narrow options, but your own environment may contain different code, policies, or attack patterns. Pilot the model on representative tasks, then review its errors before granting access to live workflows. Choose the model that passes a task-specific pilot with acceptable errors, not the one with the most impressive single score.
What Does AI Mean for Cybersecurity Jobs and the Field?
AI is changing parts of cybersecurity work, but employment projections and practitioner views do not point to a field that is disappearing. The U.S. Bureau of Labor Statistics projects 29% employment growth for information security analysts from 2024 to 2034, with about 17,300 annual openings. That is a field-wide projection, not a promise about one person’s job.
Foundational security skills remain useful as tasks change. AI may reduce some repetitive entry-level work while creating work in validation, agent oversight, data quality, and secure AI design. Teams still need people who understand systems and can judge risk.
How AI changes cybersecurity jobs
There is no universal seven-type taxonomy for cybersecurity. Common domains include network, application, information, endpoint, cloud, identity and access, and operational technology security. The mix varies by organization and the systems it protects.
Five career paths include security analyst, incident responder, security engineer, vulnerability manager, and AI security or model-risk specialist. In a May 2026 survey, 56% of AI-using cybersecurity professionals said AI had reduced the need for entry-level roles somewhat or significantly. Yet 53% thought AI was creating new types of entry-level roles.
Also, 62% said AI had not reduced the need for foundational cybersecurity skills. Responses on stress were mixed: 48% said AI decreased work-related stress, while 32% said it increased stress. The ISC2 AI workforce research reflects views from professionals who use these tools, not every worker’s experience.
In a September 2026 archive of 193 U.S. AI-driven cybersecurity listings that stated pay, the median advertised band was $159,000 to $227,000. One Netflix security engineering listing advertised $499,000 to $900,000 and asked for experience using AI agents for security research. Those are listing figures, not typical pay or a guarantee of earnings.
Where cybersecurity practice is heading
Three trends include AI-assisted detection and response, agentic security workflows with human controls, and trustworthy AI governance for critical infrastructure. Federated learning may support model training without centralizing raw data. Quantum-resistant cryptography is a developing security concern, not a current AI remedy.
Build durable skills in networks, incident analysis, data handling, and careful validation of automated recommendations.
Those skills help you move between security domains as tools and systems change. A projected rise in job openings cannot predict which role or pay band one applicant will receive.
Conclusion
AI improves protection when its speed is matched by reliable verification and clear accountability. It can help teams process large amounts of security information, find patterns, and investigate events faster. People still need to confirm important conclusions and own actions that could affect access or business operations.
Choose one repetitive security workflow and record its current performance. Run a bounded pilot, then review errors, false positives, and staff workload before expanding. Start with one workflow, define its success and failure measures, and expand only when the results justify it.
FAQ
Can you make $500,000 a year in cyber security?
Yes, some advertised cybersecurity roles reach or exceed $500,000, but those listings are exceptional. In a September 2026 archive of 193 U.S. AI-driven cybersecurity jobs that stated pay, the median advertised band was $159,000 to $227,000. One Netflix listing offered $499,000 to $900,000. Pay depends on the role, experience, employer, and location.
What is the 30% rule of AI?
There is no universally recognized cybersecurity standard called the 30% rule of AI. A 30% figure may describe a result for one task, such as a reported reduction in patching time. That kind of result applies to its test and method, not every AI system. Check what the percentage measures before using it to guide a security decision.
Is cybersecurity a dying field?
No, cybersecurity is not a dying field. The U.S. Bureau of Labor Statistics projects 29% employment growth for information security analysts from 2024 to 2034, with about 17,300 annual openings. AI may change tasks and hiring needs, but organizations still need people to protect systems, investigate incidents, and manage risk. A broad projection cannot promise a specific job.
Is there any AI tool for cyber security?
Yes, AI appears in endpoint protection, SIEM and SOAR, next-generation firewalls, cloud security, and NDR. These tools analyze different data and support different tasks. Choose one based on the workflow you need to improve and the data your team can trust. Then measure alert quality, false positives, and the review time analysts spend.
What is the best AI model for cybersecurity?
No single AI model leads every cybersecurity task. Compare defensive patching, exploit synthesis, and resistance to indirect prompt injection as separate tests. A model’s score applies to the benchmark’s task and setup, not to all security work. Pilot promising models with representative data and review their errors before allowing them to affect live systems.
Why do people quit cybersecurity?
People may leave cybersecurity because of workload, on-call demands, alert pressure, or stress. Practitioner views on AI and stress are mixed: 48% said AI decreased work-related stress, while 32% said it increased stress. Those survey results do not explain every departure. Workload, team support, role demands, and career options can all shape an individual’s choice.
What are 5 careers in cybersecurity?
Five cybersecurity careers are security analyst, incident responder, security engineer, vulnerability manager, and AI security or model-risk specialist. Analysts review security events, while incident responders help contain and recover from attacks. Engineers build and maintain defenses, and vulnerability managers track weaknesses. AI security specialists assess risks tied to models and AI systems.
What are the top 3 trends in cybersecurity?
Three major trends are AI-assisted detection and response, agentic security workflows with human controls, and trustworthy AI governance for critical infrastructure. AI can help teams review more signals, while agents can carry out approved steps. Governance sets limits, ownership, and review rules. Each trend depends on clear policies and people who can assess the results.