A sudden disconnect in the middle of a match can feel personal, but it does not by itself prove that anyone targeted you. Your connection can fail for many reasons, including a game service outage or trouble at home. The difference matters when you decide what to check next.
For gamers, even a brief interruption can spoil a close match or keep friends from playing together. A connection problem can affect one player, a household, or many players at once. This article explains what the term means and how to respond without treating every lag spike as an attack.
A disruption can come from an attack on the game service or from a problem closer to home. Knowing that difference helps you choose a useful first step instead of guessing who caused it.
Key Takeaways
- Lag alone does not prove anyone targeted you.
- A service issue can affect many players at once.
- Your home connection can face a separate problem.
- Check the provider’s status page when a match drops.
- Protect your accounts, devices, and home router.
What Does DDoS Mean in Gaming?
A DDoS attack tries to make an online service unavailable by sending it more traffic or connection requests than it can handle. The name means distributed denial of service, because traffic comes from many sources. Distributed is the key idea.
A DDoS attack can slow a game service or stop players from reaching it. It does not automatically mean that someone broke into the service or took data. A rise in traffic can also come from a real event, such as a popular game launch.
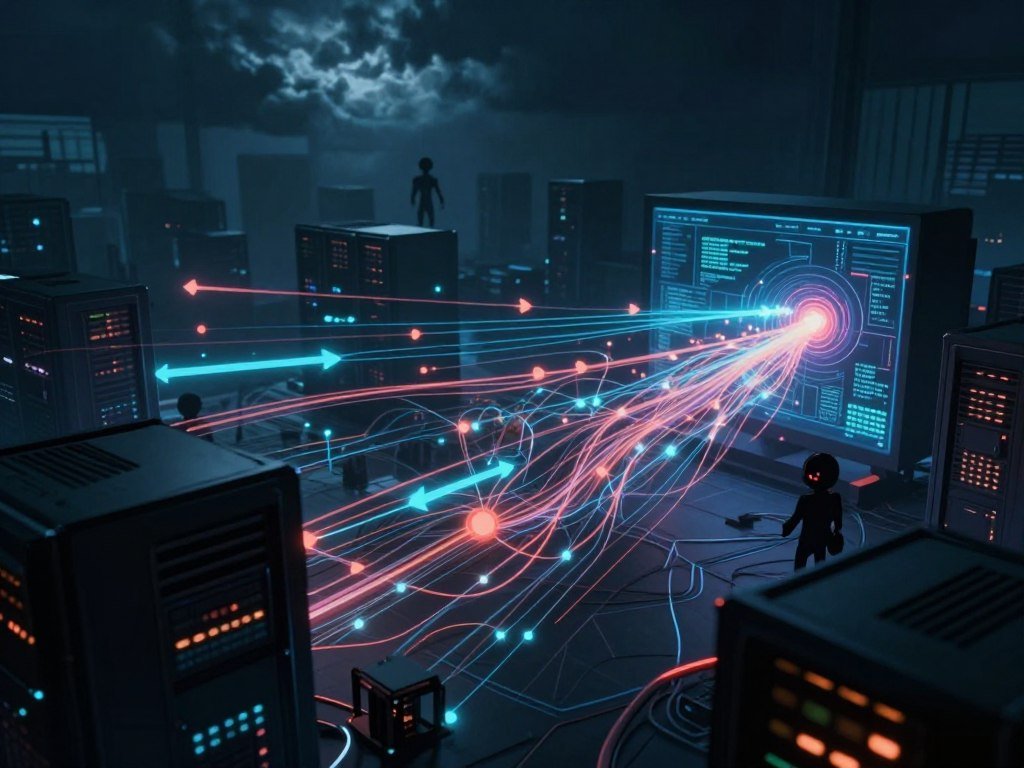
How a botnet sends traffic
A botnet is a group of internet-connected devices infected with malware and controlled remotely to send traffic at an attacker’s direction. It may include computers, phones, and other connected devices. Owners may not know their devices are involved.
Many devices can send requests at once, making the traffic harder to sort from normal activity. Not every DDoS attack relies on a botnet. Some attacks use uninfected devices or other ways to send unwanted traffic.
These attacks can use ordinary network protocols, including HTTP and TCP. Those protocols help websites and services exchange information every day. The protocol itself does not show whether traffic is harmful.
A DDoS attack does not have to enter a system or take data to deny access.
Why legitimate players cannot get through
A game service has limits on the traffic and requests it can handle at one time. When unwanted requests use too much of that capacity, real players may wait or fail to connect.
The service may still be running, yet players cannot reach its login system, match servers, or other features. A game can also depend on outside network providers, which adds more points where access can fail.
The CISA guide to DDoS attacks groups common methods into traffic-volume, protocol, and application-layer types. Each type puts pressure on a different part of a service.
The defining feature is traffic arriving from multiple sources, not simply one player having a poor connection.
Which Gaming Systems Can a DDoS Attack Target?
An attacker can aim at the game service itself, the infrastructure it relies on, or a player’s internet connection. The target shapes how wide the disruption may reach.
A game service attack can affect many players, while an attack on one home connection may affect one household. Online games may rely on outside network providers, including AWS and Cloudflare, to support their services.
Game services and their network providers
An attack on game servers can interrupt access for players using that service. A problem at an upstream provider may spread to several services that depend on its network.
That can include gaming, voice chat, or other online tools. A streaming service can also be disrupted if an attack reaches its service infrastructure, even when a player’s home connection works.
For example, free-to-play games across devices can connect players through online services that rely on different systems. The platform you use does not, on its own, reveal where an interruption began.
One player’s home connection
An attack aimed at your public IP address sends traffic toward your home router or the network serving it. Your public IP address is the address other systems can see when your home connects to the internet.
In that case, other people in your household may also have trouble getting online. The game service could remain available to everyone else. An ISP can help investigate problems that affect your home connection.
| Target | Where traffic goes | Who may be affected | First useful contact |
|---|---|---|---|
| Game service | Game servers | Players using that service | Game provider status page or support |
| Upstream provider | Provider network | Several dependent services | Affected service provider’s status page |
| Individual connection | Home router or public IP address | One household | ISP |
If several players lose access at once, a service-side problem is more plausible than a problem isolated to one home.
What Does a DDoS Attack Feel Like During a Match?
A targeted player may see sudden lag or a lost connection, while a server-side disruption can affect many players at once. Those signs are clues, not proof of a DDoS attack.
Lag, dropped matches, and lost access can have causes other than an attack. A shaky Wi-Fi signal, a busy home network, or a temporary game issue can interrupt play too.
In Rocket League, players sometimes use DDoS to mean lag or connection trouble. That casual use does not confirm that anyone launched an attack. The same is true when one match feels unstable.
A 2021 DDoS attack against top-ranked Apex Legends players disrupted competitive play. DDoS attacks have also forced a League of Legends tournament to pause. In December 2014, disruptions to Sony PlayStation Network and Xbox Live affected 160 million gamers over three days at Christmas.
| Situation | Typical reach | Useful check | What it suggests |
|---|---|---|---|
| Suspected service attack | Multiple players or services | Provider status page | Shared service issue |
| Local connection trouble | One household or device | Test other devices and services | Local network or ISP issue |
| Ordinary match instability | One game session | Try another match and check game notices | Temporary game problem |
Use these checks before deciding what the problem might be:
- Check whether other players are affected.
- Test another online service.
- Check the game provider’s status page.
- Note when the interruption began and which devices are affected.
Treat a symptom as a clue, then check whether the problem extends beyond one match or one device.
Why Do Attackers Target Games?
A player may launch an attack to knock a rival out of a match, while other attackers target providers for broader disruption or financial gain. Personal disputes and attacks on a company are different situations.
Some attackers want a competitive edge, while others seek money, attention, or wider disruption. A player may target a rival after a loss or argument. An attack on a game provider can affect people who had no part in that dispute.
Competitive advantage and retaliation
Some players use attacks to disrupt an opponent’s connection during a match. That may help the attacker gain an unfair advantage, especially in a ranked game or tournament.
Retaliation can follow a match, online argument, or team dispute. Federal law-enforcement officials have described competitive advantage as a common motive in gaming-related cases.
FBI findings on DDoS-for-hire services also describe business disputes and retaliation as reasons for attacks. Some people launch DDoS attacks for hire, rather than directing them at a personal rival.
Money, disruption and other motives
Attackers may seek revenue by selling attack services or demanding payment to stop disruption. Others want attention, or hope to damage a company’s reputation or operations.
Gaming attacks rose 94% between 2023 and 2024. Gaming ranked fourth among the most-attacked industries in the fourth quarter of 2025.
Cloudflare mitigated 47.1 million DDoS attacks in 2025, an average of 5,376 per hour. That total covers attacks across online services, not just games.
NETSCOUT recorded more than 9.1 million DDoS attacks across 209 countries and territories in the first half of 2026. These totals show that attacks continue, but they do not identify the target of every incident.
A reported attack count across all industries does not mean that every match outage is aimed at a player.
How Can Gamers Protect Their Connection?
Start with account and device hygiene, since malicious links or cheat tools can expose information or install malware. Small habits can lower the chance of avoidable trouble.
The same home-network protections apply to Xbox Series X, Xbox One, and PlayStation 5. On each console, DDoS in gaming means an attempt to disrupt a service or connection with unwanted traffic.
Protect your accounts and devices
Use these five practices to protect your security and reduce exposure:
- Avoid posting your public IP address in chats, streams, or public profiles.
- Use strong, unique passwords for gaming accounts and turn on multifactor authentication.
- Avoid unknown links and cheat tools, which may carry malware.
- Install updates for your operating system, games, and security software.
- Update your home router’s firmware, and contact your ISP if you suspect an attack.
Unknown cheat tools can ask for account details or install software without clear warning. Keep your device security tools active and use official game stores when possible.
Reduce exposure of your home connection
A virtual private network, or VPN, can mask your public IP address from some other parties. It cannot protect a game service from an attack, and it may add connection latency.
A VPN also will not fix an outage on the game provider’s side. It changes part of the route your connection takes, which can affect how quickly game data travels.
Restarting a router does not guarantee a new public IP address. The ISP and type of connection determine how an address is assigned, so repeated restarts may leave it unchanged.
Router security guidance stresses updates and safe setup for home networks. Your ISP can help review an ongoing connection problem or explain its address settings.
If your connection remains disrupted, contact your ISP rather than assuming that repeated router restarts will resolve it.
What Can Game Providers Do to Limit Disruption?
Game providers can reduce the impact by filtering malicious traffic and spreading legitimate requests across available infrastructure. Layered defenses help protect different parts of a service.
No single defense can promise that every match stays online. Providers need to watch network activity, prepare for incidents, and have a clear response plan.
Filter and distribute incoming traffic
Traffic-scrubbing services check incoming traffic and remove requests that appear harmful. A content delivery network, or CDN, can spread content across servers closer to players.
Load balancing shares requests across available servers instead of sending them all to one place. These tools can help keep a game service reachable when traffic shifts or rises.
Rate limiting caps how many requests a user or system can make in a set time. A web application firewall can filter certain requests aimed at a website or application layer.
The CISA, FBI, and MS-ISAC guidance recommends monitoring and filtering traffic, using mitigation services, and planning a response. Providers must choose tools that fit their own network and services.
Prepare for short, intense attacks
Some attacks last only seconds, so a slow response can still interrupt a match. A 2025 DDoS attack mitigated by Cloudflare peaked at 31.4 Tbps and lasted 35 seconds.
NETSCOUT found that direct-path methods made up 64.40% of attacks it observed in the first half of 2026. Attacks lasting one minute or less rose to 3.1% in that period, up from 1.6% in the second half of 2025.
Those short bursts make quick detection important. Teams can set alerts, assign response roles, and practice how to limit harm without blocking legitimate players.
Fast detection matters because even a brief attack can interrupt a match before a slower response begins.
A clear status update can help players distinguish a provider-side incident from a problem with their own connection.
Conclusion
A DDoS attack denies access by overwhelming a service or connection, but a disconnect alone cannot tell you which one is affected. Lag can point to a problem, but it does not prove someone targeted you.
Protecting your accounts and devices helps reduce avoidable exposure. It also makes it harder for malware or stolen login details to create another problem while you are trying to play.
When a match drops, check whether the game provider has posted a service notice. Then test another online service on your network to see whether the trouble reaches beyond that game.
Check the game’s status page and test another online service before deciding whether to contact the ISP.
FAQ
Is a DDoS illegal?
Yes, intentionally disrupting a protected computer or service can violate the Computer Fraud and Abuse Act in the United States. Playing a game does not make the conduct lawful. The law can apply even when an attacker claims the act was a prank or a way to win a match. The details of a case can matter.
How do you tell if you’re getting ddosed?
Lag alone does not show that you are facing a DDoS attack. Check whether several players or online services have trouble at the same time, then compare the game provider’s status page with other devices on your home network. If only one game session fails, that points to a narrower problem, but it still does not identify the cause.
How bad is a DDoS attack?
A DDoS attack can cause anything from lag and dropped matches to a full service outage. The impact depends on what the attacker targets and how long the disruption lasts. A problem aimed at one connection may affect one household, while a service-side incident can keep many players from logging in or joining games.
What is the biggest DDoS attack in history?
A 2025 attack peaked at 31.4 Tbps and lasted 35 seconds, but that figure should not be treated as an unqualified all-time record. Attack reports may measure different things, including peak traffic and attack duration. A very high peak also does not tell you how long users experienced service trouble.
Do people still do DDoS attacks?
Yes, DDoS attacks continued to be recorded in 2025 and the first half of 2026. Reported totals included millions of attacks across many industries, countries, and territories. Those broad figures do not mean that every incident targeted gaming, and they cannot show whether a particular player was singled out.
Can you give me an example of a DDoS attack?
The December 2014 disruption of Sony PlayStation Network and Xbox Live is one example. It affected 160 million gamers and lasted three days over Christmas. The event affected major online gaming services, rather than just one player’s home connection. A single player’s disconnect, by contrast, does not prove that a similar attack is underway.



