
What if the security tool guarding your network cannot see the attack unfolding right in front of it? That question drives every honest discussion of endpoint detection and response limitations. EDR is a core part of security operations, and for good reason. It watches processes, files, registry keys, and network connections in real time, then flags behavior that looks malicious. But no sensor sees everything, and treating EDR as a force field rather than a camera with a specific field of view is how organizations get surprised.
This article takes a balanced look at what EDR genuinely cannot do well, why those gaps exist at an architectural level, and how security teams work around them. The goal is not to dismiss EDR but to describe its edges precisely, because knowing the edges is what separates a mature security program from one that assumes coverage it never had.
What EDR Actually Sees, and Why That Matters
EDR works through an agent installed on the host. That agent collects telemetry: process creation, command-line arguments, file modifications, registry changes, loaded modules, and network flows. Detection logic then compares that stream against known-bad signatures, behavioral rules, and increasingly, machine-learning models.
The first limitation flows directly from this design. Everything EDR knows arrives through the agent’s observation layer. If an event never produces observable telemetry, or the agent cannot reach the layer where the event happens, the tool is blind by construction. This is not a bug to be patched. It is the shape of the technology.
Security teams that understand this stop asking “is EDR working?” and start asking “what falls outside its field of view?” That reframing is the foundation for everything below.
Limitation 1: Unmanaged and Agentless Assets
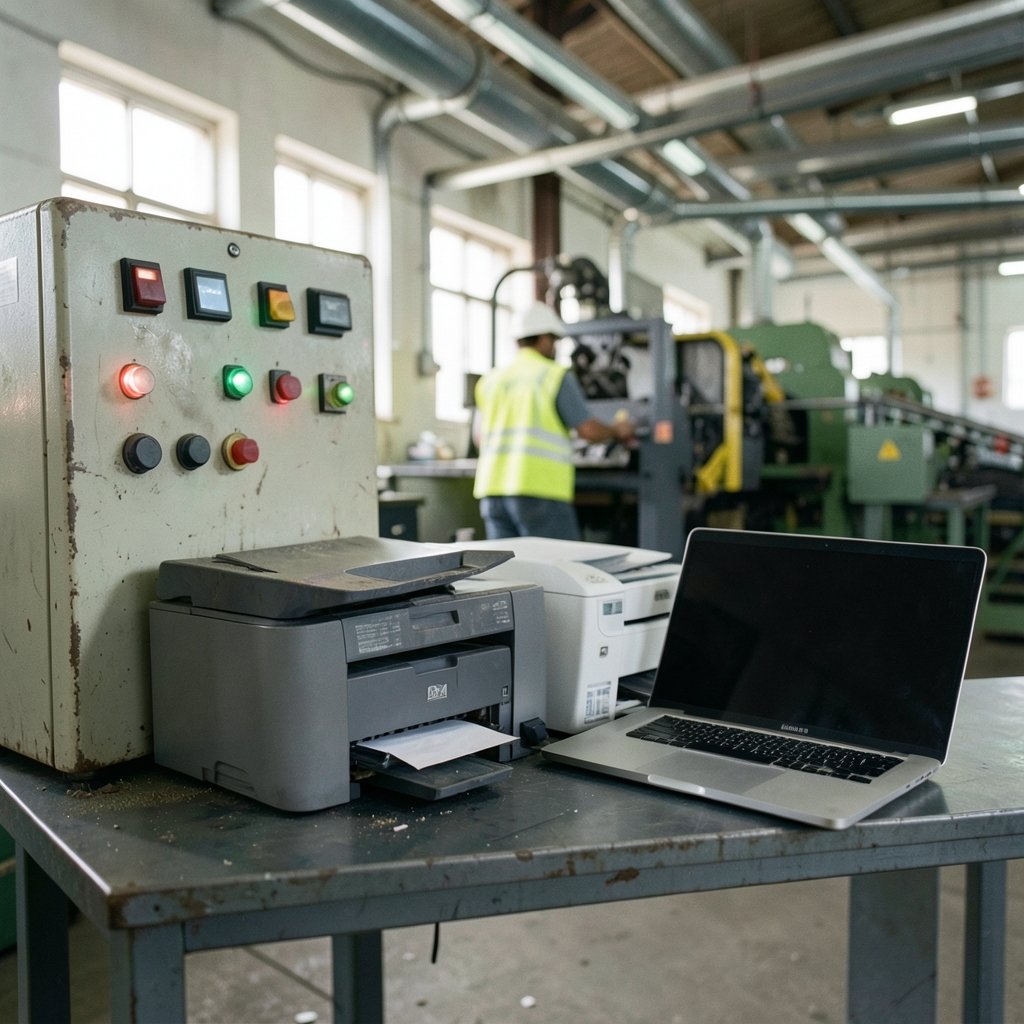
IoT sensors, operational technology on factory floors, printers, and unmanaged bring-your-own-device laptops typically cannot run an EDR agent at all. Some lack the operating system support. Others would break under an agent’s overhead. Still others belong to guests or contractors who will never consent to monitoring.
The result is a coverage map with holes. Attackers know this and deliberately pivot toward these assets as footholds. A compromised smart camera or an unpatched industrial controller can serve as a launch point into segments where EDR has no presence. The same logic applies to shadow IT: servers spun up by a business unit without security review often run agentless for months.
Practical mitigation means pairing EDR with network detection and response and passive asset discovery, so unmanaged devices still generate some signal. Many teams also maintain a hard inventory of what cannot be instrumented, because an unknown blind spot is far more dangerous than a documented one.
Limitation 2: Threats Below the Agent’s Layer
Rootkits, bootkits, and firmware implants operate beneath the level where user-mode EDR agents live. A sophisticated implant that hooks low-level system calls or persists in firmware can, in principle, hide activity from the very tool meant to catch it. Academic research on kernel-level evasion has documented these techniques for years, and firmware security remains a specialized discipline largely separate from mainstream EDR.
This does not mean every attacker deploys firmware implants. Most do not. But it does mean EDR is not a complete answer to persistence, and organizations with high-value targets should add secure boot verification, firmware integrity monitoring, and hardware-rooted attestation to their stack.
Limitation 3: Living Off the Land Blends In
One of the sharpest practical limits is behavioral. Attackers increasingly avoid custom malware and instead abuse native operating system tools: PowerShell, Windows Management Instrumentation, certutil, and dozens of other legitimate binaries. This technique, catalogued extensively in MITRE ATT&CK, is called living off the land.
The problem is definitional. If an administrator and an intruder both run the same signed Microsoft binary with similar arguments, behavioral detection must distinguish intent from context. That means higher false-negative rates on one side and alert fatigue on the other. Tuning helps, but the fundamental ambiguity never disappears. Detection engineering for LOLBin abuse relies heavily on baselining what is normal in a specific environment, which is labor-intensive and never quite finished.
Limitation 4: Alert Volume Versus Analyst Capacity
EDR generates a lot of signal. A mid-sized organization can see thousands of alerts per week, and only a fraction warrant investigation. The widely reported consequence is alert fatigue: analysts drown, triage shortcuts creep in, and genuine detections slip past exhausted reviewers.
This is an operational limitation as much as a technical one. A tool that detects everything but cannot be staffed to investigate it delivers less real protection than its detection rate suggests. Teams that get results typically invest in automation, alert correlation, and managed detection services rather than buying more sensors alone. The lesson is uncomfortable but true: EDR effectiveness depends on the people and processes behind it, and on the software.
Limitation 5: Fileless, In-Memory, and Encrypted Activity
Memory-only attacks that never touch disk leave fewer artifacts for host telemetry to capture. Encrypted command-and-control channels hide payload content even when the connection itself is visible. EDR can sometimes catch these through memory scanning and behavioral heuristics, but visibility is genuinely reduced compared with traditional file-based malware.
This is one reason extended detection and response platforms emerged, correlating endpoint signals with identity, cloud, email, and network telemetry. The endpoint alone tells an incomplete story. If you want a sense of how much noise and ambiguity detection tools must sift through, the challenge of separating machine-generated artifacts from real activity shows up everywhere, from security logs to content forensics, as explored in this guide on how to spot AI-generated content.
Limitation 6: Host-Centric Blindness to Lateral Movement
EDR watches each host. Lateral movement happens between hosts. A credential theft on one machine followed by remote execution on another produces two locally plausible events that only become suspicious when viewed together. Without a SIEM or XDR layer stitching telemetry across the estate, that cross-host context is missing.
Correlation platforms close much of this gap, but they introduce their own complexity: data pipelines, normalization work, and storage costs. Teams running open-source stacks often spend significant effort on integration. A concrete example of that integration work appears in this walkthrough of Wazuh SIEM detection steps, which illustrates how much configuration sits between raw endpoint data and a usable alert.
Limitation 7: Tampering and Agent Disablement
Attackers actively target the EDR agent itself. Techniques range from exploiting vulnerable signed drivers, a pattern known as bring your own vulnerable driver, to using uninstall utilities with stolen credentials. Government advisories have repeatedly flagged driver-based attacks against security products, and vendor advisories document agent-tampering attempts as a routine occurrence.
Hardening helps: tamper protection, kernel-level self-defense, and alerting on agent health gaps. But any agent running on a compromised host is, by definition, running in a hostile environment. Resilience planning should assume that at least one endpoint will lose its agent at the worst possible moment.
Limitation 8: Privacy Rules and Data Minimization
Endpoint telemetry is deeply personal. It can capture browsing habits, document contents, and communication patterns. Privacy regimes built around data minimization, such as the GDPR framework described by the European Commission, can constrain what organizations collect and how long they retain it. Employee monitoring laws in some jurisdictions add further limits.
The security consequence is real: less telemetry means shallower detection and shorter investigation windows. Organizations must negotiate this trade-off explicitly, documenting what is collected and why, rather than letting either privacy or security concerns silently win.
Limitation 9: Detection Is Not Prevention
EDR responds after detection fires. Isolate the host, kill the process, quarantine the file. All of these actions depend on the detection engine recognizing maliciousness first. Dwell time before detection remains a documented gap in breach reporting, and every minute before response is a minute an attacker operates freely.
This is why EDR belongs alongside preventive controls: patching, least privilege, application allowlisting, and network segmentation. Expecting EDR to compensate for weak fundamentals is a common and costly mistake.
What Actually Works in Practice
Experienced teams treat EDR as one sensor among many and design around its limits. Several practices consistently pay off: (Cybersecurity Best Practices)
- Inventory what cannot be instrumented. Maintain a living list of agentless assets and monitor them through network telemetry instead.
- Tune before you buy more. Most alert fatigue comes from untuned rules, not insufficient coverage.
- Baseline normal behavior. LOLBin detection depends on knowing what your environment looks like on a quiet day.
- Layer preventive controls. Patching and segmentation reduce the volume of attacks EDR must catch.
- Test agent tampering. Run tabletop exercises assuming the agent on a critical host is disabled.
- Staff for the alert volume you generate. If nobody can investigate, the detection does not exist.
A common mistake is buying a second EDR product to cover the first one’s gaps. Usually the better spend is correlation, automation, and network visibility. Another frequent error is skipping retention planning, which leaves investigators without the historical data they need weeks after an incident.
The same pattern of “powerful tool, real limits” appears across security and technology. Voice cloning tools, for instance, produce impressive results but carry documented constraints, as this overview of AI voice cloning tools and their limitations describes. Recognizing a tool’s boundaries is a skill that transfers.
How EDR Compares With Adjacent Technologies
| Capability | EDR | XDR | SIEM | Network Detection |
|---|---|---|---|---|
| Primary data source | Endpoint agent | Many sources | Logs and events | Network traffic |
| Cross-host correlation | Limited alone | Strong | Strong | Moderate |
| Agentless asset coverage | Weak | Better | Good | Strong |
| Alert context depth | High on host | High across estate | Variable | Moderate |
| Typical operational burden | Medium | High | High | Medium |
The table makes the architectural story clear. Each category has a center of gravity, and the gaps of one are frequently the strengths of another. Mature programs combine them rather than searching for a single product that does everything.
Conclusion
Endpoint detection and response limitations are not a scandal. They are the natural consequence of how EDR works: an agent observing a host, generating telemetry, and matching behavior against models of maliciousness. Everything outside that loop, from agentless devices to firmware implants to cross-host context, sits beyond its reach by design.
The practical takeaway is straightforward. Deploy EDR, tune it relentlessly, staff it honestly, and surround it with controls that cover its edges: network visibility, preventive hardening, privacy-aware governance, and correlation across the estate. Security teams that speak plainly about what their tools cannot see build more resilient programs than those that assume a dashboard equals coverage. Knowing the blind spots is not pessimism. It is the beginning of real defense.
Frequently Asked Questions
What are the main limitations of endpoint detection and response?
The main limitations fall into a few categories: no visibility into agentless assets like IoT and OT devices, inability to see threats below the user-mode agent layer such as firmware implants, difficulty distinguishing living-off-the-land abuse from legitimate administration, alert volume that outpaces analyst capacity, reduced visibility into fileless and encrypted activity, limited cross-host context without a SIEM or XDR layer, agent tampering by attackers, and privacy rules that constrain telemetry collection. Each is architectural or operational rather than a simple bug.
Can EDR detect fileless malware?
Sometimes, but not reliably. Fileless attacks that live only in memory leave fewer artifacts for host telemetry to capture. EDR can catch some of these through memory scanning and behavioral rules, but detection rates are lower than for traditional file-based malware. Organizations facing this threat typically add memory forensics, network detection, and identity monitoring to compensate.
Why does EDR sometimes miss living-off-the-land attacks?
Because living-off-the-land attacks use legitimate, signed operating system tools with plausible arguments. If an administrator and an intruder both run PowerShell in similar ways, the tool must infer intent from context. That inference produces false negatives and false positives alike. Baselining normal activity in a specific environment improves detection, but the ambiguity is inherent to the technique.
Is EDR useless without a SIEM or XDR?
Not useless, but narrower. A standalone EDR sees each host well and the connections between hosts poorly. Lateral movement, credential theft followed by remote execution, and slow multi-stage intrusions become much easier to spot when telemetry is correlated across the estate. Many teams run EDR first and add correlation later, which works if the gap is understood and documented.
How do attackers disable EDR agents?
Common methods include exploiting vulnerable signed drivers to gain kernel-level control, using stolen administrative credentials with uninstall utilities, and abusing legitimate management tooling. Vendors counter with tamper protection and self-defense mechanisms, and security teams should monitor agent health so a silent gap becomes a visible alert rather than an invisible one.
Does privacy law really limit what EDR can collect?
Yes, in many jurisdictions. Data minimization principles and employee monitoring rules can restrict what endpoint telemetry is gathered and how long it is retained. The security trade-off is genuine: less data means shallower detection and shorter investigation windows. The workable approach is to document what is collected, why, and for how long, and to align security and legal teams before an incident forces the conversation.



