
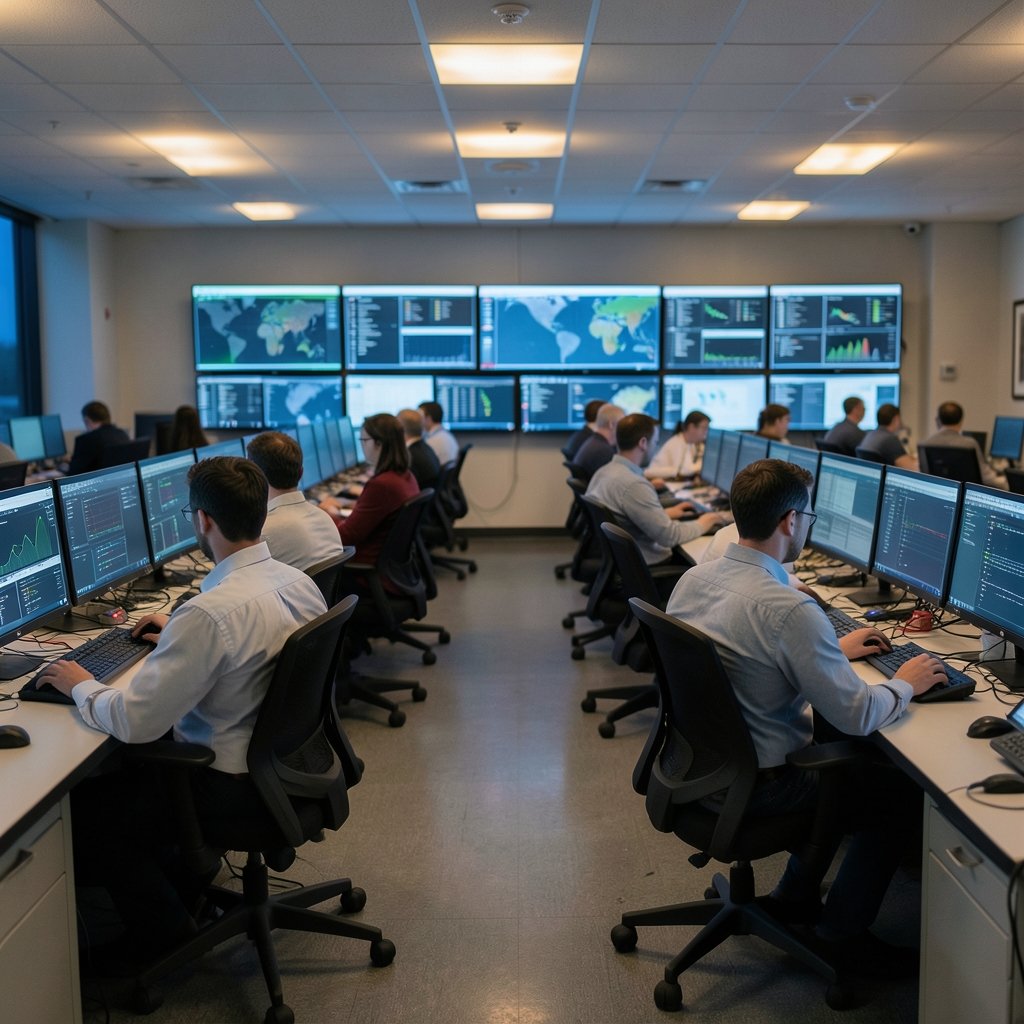
Why do security teams watch screens full of alerts while a real attack slips through? That mismatch is what security information and event management, usually shortened to SIEM, has to handle. It is one of the most purchased and least understood tools in cybersecurity. (NIST Cybersecurity Framework)
Quick Answer: What is security information event management?
Security information and event management is a category of software that collects log and event data from across an organization’s systems, normalizes it, and analyzes it in real time to detect threats and support compliance reporting. Readers encounter it in three main places: as a monitoring platform in a security operations center, as a log-retention tool for audits, and as a data source feeding automated response systems.
It is often confused with SOAR (orchestration and automated response) and EDR (endpoint detection), which handle automation and device-level telemetry rather than centralized log correlation. Before investing, compare data ingestion volume, correlation and alerting quality, retention costs, staffing requirements, cloud versus on-premises delivery, and integration coverage.
A Short Answer First, Then the Messy Reality
Ask ten vendors what SIEM means and you will get ten slightly different answers. That is not a dodge. No single standards body defines the term, so definitions drift between marketing pages, analyst reports, and practitioner forums.
Here is the practical version. A SIEM is a central nervous system for security data. It pulls logs from servers, firewalls, endpoints, cloud accounts, and identity providers. It cleans that data into a common format. Then it watches for patterns that suggest something is wrong, and it keeps everything long enough to satisfy auditors and support investigations.
The Gartner analysts Mark Nicolett and Amrit Williams are widely credited with coining the term in a 2005 report. Treat that attribution as widely repeated rather than gospel, since the original document is paywalled and rarely re-checked. What matters more is the lineage: SIEM grew out of 1990s log-management products and early SIM and SEM tools sold by vendors such as Intellitactics, netForensics, ArcSight, and e-Security. Security information management handled storage and analysis. Security event management handled real-time monitoring and alerting. The two merged, and the acronym stuck.
What SIEM Actually Does Under the Hood
Strip away the dashboards and most SIEM platforms perform six core jobs. Vendor descriptions vary, but the fundamentals are consistent.
Log aggregation and normalization
Every device writes logs in its own dialect. A firewall logs one way, a Windows domain controller another, a cloud provider a third. The SIEM ingests all of it and translates records into a shared schema so a failed login looks like a failed login regardless of source. This unglamorous step is where most deployments succeed or fail.
Correlation rules
This is the engine room. Rules stitch together events that are harmless alone but suspicious together: a failed login spike followed by a successful login from a new country followed by a large data transfer. Correlation is what separates a SIEM from a very expensive log archive.
Real-time alerting
When a rule fires, someone needs to know. Alerts route to email, ticketing systems, chat channels, or a case management workflow. Many teams pair the SIEM with dedicated case management software for law firms or security-specific ticketing so investigations do not live in someone’s inbox.
Dashboards and visualization
Executives want trend lines. Analysts want drill-downs. A good SIEM serves both without forcing anyone to write queries by hand.
Retention for compliance
Regulations demand that logs be kept and protected. The PCI Security Standards Council publishes detailed logging and retention requirements in its document library, and auditors expect evidence. The SIEM becomes that evidence locker.
Forensic search
After an incident, investigators need to ask historical questions: who touched this server last Tuesday, and from where? Fast search across months of data is a genuine differentiator between platforms.
Why Compliance Pushed SIEM Into Every Budget
Security teams rarely win budget on fear alone. Compliance wins budget. SIEM adoption accelerated because auditors needed proof that systems were monitored and logs were retained.
The U.S. government codified log management practice in NIST Special Publication 800-92, the Guide to Computer Security Log Management, published in September 2006. It predates modern SIEM terminology and does not define the acronym, but it remains the reference document for how logs should be generated, stored, and reviewed. Payment card rules added commercial pressure, and federal information security law added public-sector pressure.
The result is a tool that often gets bought for compliance and only later earns its keep for detection. That ordering matters. Teams that treat SIEM as an audit checkbox tend to underinvest in tuning, and an untuned SIEM is a very loud, very expensive paperweight.
The Market Shift: From Appliances to Cloud
For years, SIEM meant racks of appliances and a licensing model based on daily log volume. That model punished success. The more data you sent, the more you paid, so teams filtered aggressively and sometimes filtered away the evidence they needed.
Cloud-delivered SIEM changed the math. Splunk Cloud, Microsoft Sentinel (launched in 2019), and Google Chronicle pushed the category toward subscription pricing and elastic storage. Gartner also changed how it covers the market, retiring its long-running SIEM Magic Quadrant after 2022 in favor of other report formats. Exact transition dates are worth confirming directly with Gartner if a purchasing decision hinges on them.
The cloud shift created a new problem: identity. Service accounts, API keys, and automation tokens now outnumber human users in many environments, and they generate events that traditional correlation rules were never designed to catch. That gap is why tools for non-human identity security have become a natural companion to SIEM rather than a competitor.
SIEM vs. SOAR vs. EDR: Clearing Up the Confusion
The acronym soup causes real purchasing mistakes. Here is the honest comparison.
| Capability | SIEM | SOAR | EDR / XDR |
|---|---|---|---|
| Primary job | Collect, correlate, alert | Automate and orchestrate response | Detect and respond on endpoints |
| Data scope | Broad: logs from everywhere | Consumes SIEM and other alerts | Narrow: device and workload telemetry |
| Typical user | SOC analyst, compliance lead | Automation engineer | Endpoint analyst |
| Strength | Visibility and retention | Speed and consistency | Deep host-level detail |
| Weakness | Alert volume, tuning cost | Needs clean inputs to work | Limited cross-system context |
Gartner is generally credited with coining SOAR around 2017, though the primary source is hard to verify. The practical relationship is simple: the SIEM sees, the SOAR acts, and the EDR supplies the richest endpoint detail. None replaces the others.
What Actually Works in Practice
First-hand experience across security operations points to a few patterns that separate working SIEM deployments from expensive failures.
Start with five use cases, not five hundred. Teams that enable every out-of-the-box rule on day one drown immediately. Pick detections tied to real risks: impossible travel, privilege escalation, malware beaconing, data exfiltration, and unauthorized configuration changes. Expand only after those run clean.
Budget for tuning, not only licensing. Analyst commentary and practitioner forums repeat the same finding: alert fatigue and skilled-staff shortages are the persistent failure modes. A common rule of thumb is that every dollar of license spend needs a matching investment in people and rule maintenance. Skipping that step is the single most common mistake.
Normalize before you scale. Every messy log source compounds later. Fix parsing early, document your schema, and resist the urge to onboard everything at once.
Watch retention costs like a hawk. Hot storage for fast search is expensive. Tier older data to cheaper storage and keep the hot window tight.
Test your detections. Run a known attack simulation quarterly and confirm the SIEM catches it. Untested rules rot silently.
Do not ignore physical and endpoint layers. Digital logs tell half the story. Teams responsible for facilities often pair monitoring with home security systems and smart locks for home security on the residential side, and the same principle applies commercially: layered visibility beats a single chokepoint. For remote workers and small offices, outdoor security cameras without a subscription fill gaps that log data cannot.
Common Mistakes That Sink SIEM Projects
The failure patterns are remarkably consistent. Teams buy before defining requirements. They underestimate ingestion volume because they forgot cloud flow logs and DNS. They staff the tool with one overworked analyst. They let the compliance deadline drive the rollout instead of a risk assessment. They treat the SIEM as a detection product when half its value is investigation and retention.
A quieter mistake: ignoring the broader security stack the SIEM depends on. A SIEM cannot correlate what it never receives. If endpoint coverage is thin or network security is weak, the SIEM will faithfully report on a partial picture. Reviewing internet security fundamentals alongside SIEM planning keeps expectations honest.
Is SIEM Still Worth It?
Yes, with conditions. The category is not dying, but it is consolidating and specializing. Pure log archiving has been commoditized by cloud providers. The durable value sits in correlation quality, investigation speed, and integration breadth.
Buyers should also expect terminology drift. Vendors increasingly bundle UEBA (user behavior analytics) and SOAR into “SIEM” platforms, so two products with the same label may do very different things. Read the data sheet, not the category name. Ask specifically: what does ingestion cost at our projected volume, how many rules ship tuned, what is the mean time to onboard a new source, and who maintains the content?
For organizations with regulated data, a real security operations function, or both, a SIEM remains close to mandatory. For a twenty-person company with no dedicated security staff, a managed detection service built on someone else’s SIEM is usually the smarter buy.
Conclusion
Security information and event management is best understood as a discipline wrapped in software: collect everything, normalize it, correlate it, alert on it, and keep it long enough to answer hard questions later. The technology has moved from appliances to cloud platforms, and its boundaries have blurred with SOAR, EDR, and identity tools. What has not changed is the core lesson. A SIEM is only as good as the data feeding it and the people tuning it. Buy for visibility, staff for tuning, and measure whether it actually catches the attacks you care about.
Frequently Asked Questions
How is SIEM different from a firewall?
A firewall blocks or allows traffic at a boundary. A SIEM watches everything after the fact, across many systems, and looks for patterns that suggest compromise. Firewalls enforce policy; SIEMs provide visibility and detection. Most organizations need both, and the SIEM typically ingests the firewall’s logs.
Does a small business need a SIEM?
Usually not as a standalone purchase. The licensing, tuning, and staffing costs rarely make sense below a certain scale. A managed detection and response service that runs a SIEM on the customer’s behalf is the more practical route for small teams with compliance obligations.
What does SIEM stand for?
It stands for security information and event management. The name reflects two merged product categories: security information management, which handled log storage and analysis, and security event management, which handled real-time monitoring and alerting.
How much does a SIEM cost?
Costs vary enormously with data volume, delivery model, and retention. Pricing is typically tied to daily ingestion or storage, which means the biggest budget risk is underestimating how much data you will send. Always model cloud flow logs, identity provider events, and endpoint telemetry before signing.
Can a SIEM stop an attack on its own?
No. A SIEM detects, alerts, and preserves evidence. Stopping an attack requires a response capability, whether that is a human analyst, an EDR tool, or a SOAR platform executing automated actions. Treating detection as prevention is a common and costly misunderstanding.
Why do SIEM projects fail so often?
The recurring causes are alert fatigue from untuned rules, underestimated data volume, insufficient staffing, and unclear requirements at purchase time. Projects that start with a small set of high-value use cases and a dedicated tuning budget succeed far more often than broad, deadline-driven rollouts.



