

What happens to your email, bank, and cloud accounts if the one tiny USB key that gives access to them disappears in a taxi or gets washed with a pair of jeans? That question separates people who own a security key from people who own one and sleep well at night.
Hardware security keys are among the strongest defenses against phishing because they bind a login to a physical device. But that same physicality creates a new failure point: lose the key, lose access. A real backup strategy is not an optional extra. It is the other half of the security decision. This guide walks through what actually works in practice, the mistakes that catch people out, and how to build a plan that survives a lost key, a broken key, and a stolen key.
Why a Single Security Key Is a Trap
A security key works by proving that the person logging in has the physical device. It resists phishing because the key checks the website’s real address before it signs anything. That is why security teams push so hard for them. A report from the FIDO Alliance describes how these standards were built to replace passwords with phishing-resistant sign-in. (Use Strong Passwords)
The catch is obvious once you think about it. If the only key to your account is a piece of plastic on your keyring, then your account security is now tied to your house keys, your bag, and your laundry routine. The Cybersecurity and Infrastructure Security Agency has repeatedly warned that any single authentication factor can become a single point of failure, and its guidance on phishing-resistant sign-in points toward enrolling more than one authenticator.
In practice, the people who get locked out are rarely victims of sophisticated attacks. They are ordinary users who registered one key, put it in a drawer, and lost the drawer.
The Core Principle: Register at Least Two Keys
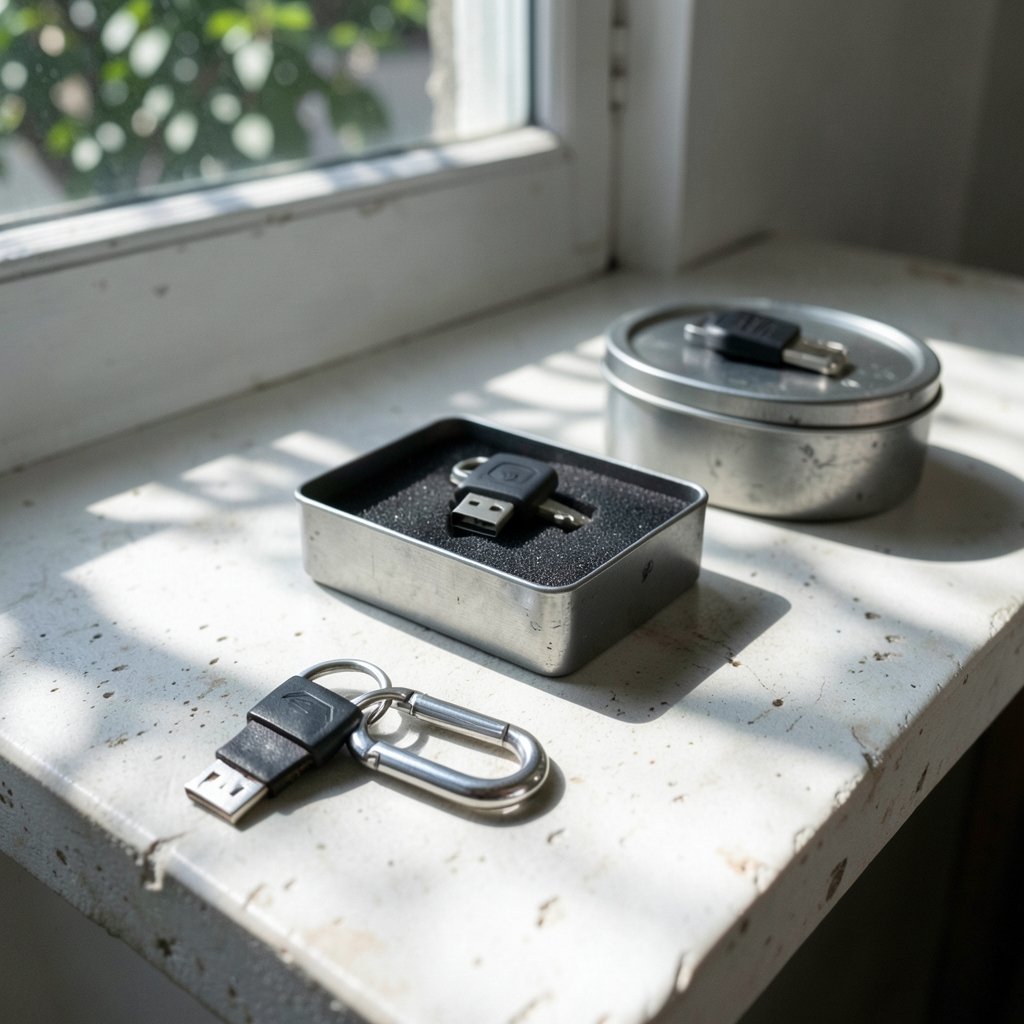
The simplest and most effective rule is to register at least two keys on every important account. One lives with you and travels daily. The other lives somewhere safe and rarely moves.
Most major providers allow multiple keys per account, though the exact limit varies. Google, Microsoft, and GitHub all let users add several security keys to a single account. The number matters less than the habit: two keys, two locations, one account.
| Setup | Keys registered | Where they live | Risk level |
|---|---|---|---|
| Single key only | 1 | On your keyring | High |
| Good baseline | 2 | One carried, one stored | Low |
| Stronger setup | 3 | Carried, home safe, off-site | Very low |
| Overkill for most | 4+ | Scattered | Adds confusion |
A third key is worth considering for accounts that would be catastrophic to lose, such as a primary email address that everything else resets through. That third key can sit at a relative’s house or in a safe deposit box.
Which Accounts Deserve a Backup Key First?
Not every account needs the same treatment. Rank them by what a lockout would cost you. Start with the accounts that can reset all the others.
- Primary email address, because password resets for everything else flow through it.
- Password manager master account, because it holds the rest of your credentials.
- Banking and payment apps.
- Cloud storage holding irreplaceable files.
- Social accounts tied to your identity or business.
That ordering is not arbitrary. If someone controls your email, they can often reset everything else. If you lose access to your email, you may lose the ability to recover anything. Treat it as the crown jewel.
Choosing the Right Backup Key
Not all keys are equal, and the backup does not have to be identical to your daily driver. The main split is between keys that store credentials on the device and keys that only act as a second factor.
FIDO2 resident credentials live on the key itself. If that key is lost, the credential is gone and you must re-enroll. Non-resident keys work more like a smart second factor and do not store the credential. The distinction matters because it shapes how much a lost key hurts.
Practical buying advice that saves headaches:
- Buy two keys from the same brand and model if possible, so behavior is predictable.
- Choose keys with both USB-A or USB-C and NFC if you use a phone for sign-in.
- Prefer keys that support a PIN, which protects a stolen key from being used by someone else.
- Avoid cheap no-name keys with unclear firmware support, since they may not receive security updates.
If you also carry backup drives for your data, the same logic of redundancy applies. A look at the best external hard drives for backup shows how the storage world handles the same trade-off between convenience and resilience.
Storing Backup Keys Without Creating a New Risk
A backup key is only useful if it survives the disaster that takes out your primary key. That means it should not live in the same bag, the same house fire zone, or the same pocket.
What actually works:
- Keep the backup key in a locked drawer or safe at home, separate from the primary key.
- Store a second backup off-site, such as with a trusted family member or in a safe deposit box.
- Label keys physically so you know which is which, but never write account names on them.
- Keep a written record of which accounts use which key, stored securely offline.
A common mistake is storing the backup key right next to the recovery codes. If a burglar finds that drawer, they get both the key and the codes. Split them up. The key goes in one place, the codes in another.
Another mistake is registering a backup key and then never testing it. Keys can fail silently after firmware updates or provider changes. Test the backup key at least twice a year by actually signing in with it. A backup you have never used is a hope, not a plan.
Recovery Codes: The Unsung Backup Layer
Even with two keys, recovery codes remain the last line of defense. Most providers generate a set of one-time codes when you enable two-factor authentication. These codes work when every key is lost, broken, or left at the office.
Treat recovery codes as seriously as the keys themselves:
- Print them and store them offline. A file on the same laptop you sign in from is not a backup.
- Store them in a second location from your backup key.
- Regenerate them after using one, and after adding or removing a key.
- Check expiry dates, since some providers rotate codes.
The National Institute of Standards and Technology treats authenticator recovery as a core part of digital identity guidance, and its publications on authentication stress that recovery paths must be planned, not improvised. If a provider offers a recovery method that is weaker than the key itself, such as SMS, know that this is the weakest link in your chain.
Enterprise and Team Considerations
For organizations, key backup is a policy problem as much as a technical one. Identity platforms such as Microsoft Entra, Okta, and Google Workspace document administrative recovery flows, including temporary access passes and admin-initiated resets.
A sensible team policy covers four things:
- Every employee enrolls at least two keys before the first one is used for work.
- IT keeps a documented, audited process for resetting a lost key.
- Recovery codes are issued and stored according to a written standard.
- Departing staff hand back keys, and those keys are removed from accounts immediately.
The security posture of a whole organization can hinge on one person’s key management. The same principle shows up in device security more broadly, where the key differences between Android and iPhone security determine how much a lost device exposes. (Security token)
What to Do When a Key Is Lost or Stolen
Act fast, and act in the right order. The steps below work for most providers.
- Sign in with your backup key or a recovery code from a trusted device.
- Remove the lost key from every account it was registered to.
- Register a replacement key immediately.
- Regenerate recovery codes, since the old set may have been exposed.
- Review recent account activity for anything unusual.
- Change the password on any account where the key was the only second factor.
If the lost key required a PIN, the risk of misuse is lower, but removal is still the priority. A stolen key plus a stolen PIN is a serious combination, and speed is the best defense.
For people who manage money online, a lockout can be more than an inconvenience. Understanding instruments like a home equity loan versus a line of credit is one thing, but losing access to the account that services it is another. Account recovery planning belongs in the same conversation as financial planning.
Common Mistakes That Undo a Good Strategy
Even careful people trip on the same handful of errors. Watch for these.
Registering a backup key and never labeling it. Six months later, nobody remembers which key is which. Physical labels solve this cheaply.
Storing both keys together. A single lost bag can then defeat the whole plan. Keep them in separate locations, not merely separate pockets.
Relying on a phone as the only backup. Phone-based authenticators are convenient, but a lost or wiped phone is a common lockout cause. A hardware key in a drawer is more reliable.
Forgetting the recovery email. If the recovery address is an old account you no longer check, the whole chain breaks. Verify it works.
Skipping the test. Untested backups fail at the worst moment. Put a reminder in your calendar twice a year.
Ignoring firmware updates. Some keys need occasional firmware updates for security fixes. Check the vendor’s guidance and update when possible.
Building a Simple, Repeatable Routine
A backup strategy does not need to be complex. It needs to be repeatable. Here is a routine that takes about an hour to set up and a few minutes to maintain.
- Buy two keys from a reputable brand.
- Register both on your top five accounts.
- Store one key at home in a safe place and one off-site.
- Print recovery codes and store them separately from both keys.
- Set two calendar reminders a year to test the backup key.
- Review the plan whenever you add a new important account.
That is it. No elaborate system, no expensive hardware beyond the keys themselves. The people who stay secure are not the ones with the most gadgets. They are the ones who planned for the day the gadget disappears.
If you are also thinking about broader resilience, the same redundancy mindset applies to power and data. A guide to the best home generators for reliable backup power makes the same point: the backup only matters if it works when the primary fails.
Conclusion
A hardware security key is one of the best security upgrades most people can make. But a single key is a single point of failure, and the strongest lock in the world is useless if you cannot get through the door. The winning strategy is boring and effective: register at least two keys, store them in separate places, keep recovery codes offline, and test the backup before you need it. Do that, and a lost key becomes a minor annoyance instead of a crisis.
Frequently Asked Questions
How many security keys should I register per account?
At least two, and three for your most critical accounts such as primary email. One key travels with you, one stays in a safe place, and a third can live off-site. Most major providers allow several keys per account, though limits vary.
What happens if I lose all my security keys?
You fall back on recovery codes, which is why storing them offline and separately from your keys matters so much. If you have no codes and no backup key, you must contact the provider’s support team and prove your identity, which can take days or longer.
Is a phone authenticator a good enough backup for a hardware key?
It is better than nothing, but it is not equivalent. Phones get lost, wiped, or replaced, and app-based codes can be phished in ways hardware keys resist. A spare hardware key in a drawer is the more reliable backup.
Should I store my backup key with my recovery codes?
No. Keeping them together means one theft or one house fire destroys both layers of protection. Store the key and the codes in separate, secure locations.
Do backup keys need to be the same brand as my main key?
Not necessarily, but matching brands and models makes behavior predictable and simplifies troubleshooting. Whatever you choose, confirm the key supports the standards your accounts require, and test it before relying on it.
How often should I test my backup key?
Twice a year is a reasonable routine. Sign in with the backup key, confirm it still works, then return it to storage. This catches firmware issues, provider changes, and forgotten PINs before an emergency forces the issue.



